04 September 2026 IT Strategy 12 min read

Business Continuity Planning: Why Every Business Needs One Now

Need IT expertise?

Let's discuss your business continuity strategy.

Get in Touch

Let me tell you a story about a business last year. A mid-sized logistics company in Hamburg. They had 120 employees, 40 vehicles, and a customer base across northern Germany. One Tuesday morning, a ransomware attack encrypted their entire ordering system. Within six hours, they couldn't process orders. Within 24 hours, three major clients started looking for alternative suppliers. Within a week, they'd lost €420,000 in revenue - and two key clients never came back.

They had a computer system. They had insurance. They even had a backup server in the basement. But they didn't have a business continuity plan.

Here's the thing: most businesses don't think about business continuity until something goes wrong. And by then, it's often too late. The question isn't if something will go wrong - it's when, and whether your business will be ready.

In 2025 and 2026, the threats are more diverse and more frequent than ever. Ransomware attacks on SMEs in the UK surged by 47% year-on-year. Power outages caused by extreme weather events disrupted businesses across Estonia and Germany. Supply chain failures - from geopolitical tensions to port closures - brought operations to a standstill. And human error? Still the number one cause of data loss, accounting for 88% of incidents according to the 2025 Data Breach Investigations Report.

So let's talk about how to prepare - practically, affordably, and without the corporate jargon.
What You'll Learn

The 5 Steps to Building Your Business Continuity Plan

Step 1: The Risk Assessment - Know What Could Go Wrong

Before you can protect your business, you need to understand what threats it faces. Not theoretical ones from a textbook - real, practical threats that could actually impact your operations.

Start by asking your team these questions:

  • What would happen if our primary server failed right now?
  • How long could we operate without our main website?
  • Who has access to our critical systems, and what happens if they leave?

Step 2: The Business Impact Analysis - Know What Matters Most

Not all systems are equal. Your email server might be important, but your ordering system is critical. Your internal wiki is useful, but your customer database is essential.

A Business Impact Analysis (BIA) helps you identify and prioritise your critical business functions. Here's how we approach it:

  • Identify critical systems - What would bring your business to a halt if it went down?
  • Define Recovery Time Objectives (RTO) - How quickly does each system need to be back online?
  • Define Recovery Point Objectives (RPO) - How much data can you afford to lose? Every 15 minutes? Every 24 hours? This determines your backup frequency.
  • Calculate the cost of downtime - The average cost of unplanned downtime for a mid-sized business is approximately €300,000 per hour. For larger enterprises, that figure climbs to millions annually.
Network infrastructure analysis for business impact assessment

The BIA tells you where to focus your resources. And more importantly, it tells you what you can afford to wait on.

Step 3: The Recovery Strategy - Build Your Safety Net

Now that you know what's critical and how quickly you need it back, it's time to build the actual recovery strategy. This is where most businesses get it wrong - they buy technology without thinking about processes, people, and communication.

A comprehensive recovery strategy covers five areas:

  • Technology recovery - Backups, redundant systems, cloud failover, disaster recovery as a service (DRaaS).
  • People recovery - Who does what when things go wrong? Do they know their roles? Have they been trained? This is where most plans fail.
  • Communications plan - How do you notify customers, suppliers, staff, and regulators? Do you have contact lists that are actually up to date?
  • Alternative operations - Can your team work from home? Do you have alternative suppliers? Can you process orders manually if your system is down?
  • Legal and compliance - What are your regulatory obligations? Do you need to notify data protection authorities? What does your insurance cover?
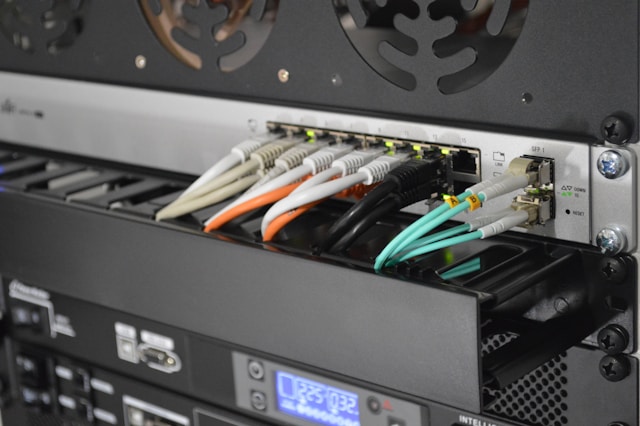
Network switch and recovery strategy implementation

At Dyonix, we build recovery strategies proportional to your risk. A small business with 10 employees needs a different plan than a manufacturing company with 500. The goal isn't perfection - it's resilience.

Step 4: Test, Test, Test - Because Plans Fail Without Practice

A business continuity plan that's never been tested is just paperwork. It looks good on paper, but when the real crisis hits, nobody knows what to do.

We recommend testing at least twice a year, with a full tabletop exercise quarterly. Think of it like a fire drill - you wouldn't wait for an actual fire to find out your fire exits are blocked.

Types of testing we use:

  • Tabletop exercises - Walk through a scenario with your team. "What would we do if our primary server crashed right now?"
  • Functional tests - Actually restore from backups. Verify the data is intact and usable.
  • Full failover drills - Switch to your backup system and run your business on it for a day.
  • Communication drills - Test your notification procedures. Do your contact lists actually work?
Testing business continuity plan with team

Most of our clients test their plans after major infrastructure changes, and we include testing as part of our ongoing managed services. The result? When a real incident happens, your team doesn't panic - they execute the plan.

Step 5: Review and Update - Because Your Business Changes

Your business continuity plan is not a one-time project. It's a living document that needs to evolve as your business grows, your technology changes, and new threats emerge.

We recommend a formal review at least twice a year, covering:

  • Has your critical infrastructure changed? New servers? New applications? New cloud services?
  • Has your team changed? New key personnel? Updated contact information?
  • Have new threats emerged? New ransomware variants? New regulatory requirements?
  • Have your test results revealed gaps? Every test teaches you something new.
  • Have your customers changed? New SLAs? New compliance requirements?

The best business continuity plans are living documents - they evolve alongside your business. And the best partners help you maintain them.

  • Do we have backups that we've actually tested restoring from?
  • What would our customers experience if we went offline for 24 hours?
  • Common Mistakes We See (And How to Avoid Them)

    After working with dozens of businesses across the UK, Germany, and Estonia, we've seen the same mistakes repeatedly. Here are the top five:

    1. Thinking "it won't happen to us" - The Hamburg logistics company thought the same thing. Ransomware doesn't discriminate by company size. Power outages don't care about your business plan. Human error doesn't wait for the right moment.

    2. Focusing only on technology - Your backup system is only as good as your team's ability to use it. We've seen perfectly configured disaster recovery systems fail because nobody knew how to operate them under pressure.

    3. No communication plan - When something goes wrong, your customers, suppliers, staff, and regulators want to know. Without a clear communication plan, you'll spend valuable time trying to figure out who to call instead of fixing the problem.

    4. Single points of failure - One person who knows everything? One server with no backup? One supplier with no alternative? These are the things that bring businesses to their knees. Build redundancy into your critical paths.

    5. Never testing - A plan that's never tested is just paperwork. Test it. Test it often. Learn from the tests. Update the plan. Repeat.

    At Dyonix, we use a structured risk assessment framework that identifies threats across four categories: technology (hardware failure, software bugs, cyber attacks), people (staff turnover, human error, key person dependency), processes (supply chain disruptions, regulatory changes), and external factors (power outages, natural disasters, geopolitical events).

    Server room infrastructure for business continuity planning

    The output? A prioritised list of risks, ranked by likelihood and impact. This becomes the foundation of everything that follows.

    Conclusion: Don't Wait for the Disaster to Build Your Shield

    Here's the bottom line: something will go wrong. The question isn't whether - it's whether your business will be ready when it does.

    Business continuity planning isn't about fear. It's about responsibility - to your customers, your employees, your suppliers, and yourself. It's about making sure that when the inevitable happens, your business doesn't just survive, but emerges stronger.

    The five steps - Risk Assessment, Business Impact Analysis, Recovery Strategy, Testing, and Review - provide a practical framework that any business, regardless of size or industry, can implement.

    And at Dyonix, we're here to help you every step of the way. From the initial risk assessment to ongoing testing and review, our team of UK, German, and Estonian experts will ensure your business continuity plan is practical, affordable, and effective.

    You may also like

    Related posts

      Scroll